Hacking a university rector's iPhone doesn't happen by accident. It happens when pressure cooker politics meets commercial surveillance tools built for nation-states.
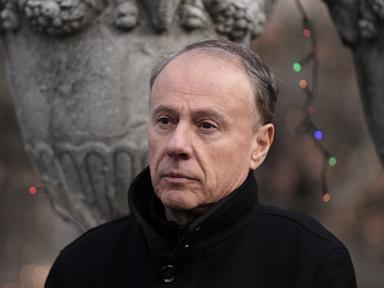
In October 2026, researchers at The Citizen Lab and Serbia's SHARE Foundation confirmed with high confidence that Vladan Đokić, rector of the University of Belgrade, had his phone infected in 2026 with Pegasus spyware made by the Israeli firm NSO Group. The timing couldn't have been sharper. The findings landed just six days before Serbia's October 25 snap parliamentary election, right in the middle of two years of student-led anti-corruption protests sparked by the deadly November 2024 railway station canopy collapse in Novi Sad. Meanwhile, you can read related stories here: What Everyone Missed About Apple's October 28 Touchscreen Laptop Event.
Honestly, this isn't just another headline about Balkan politics. It's a wake-up call about how mercenary spyware gets pointed at campus leaders, anti-corruption prosecutors, and ordinary protesters when power is on the line.
What Actually Happened To Vladan Đokić And Why It Matters
When people hear a university administrator got hacked, they usually picture a sloppy phishing email. That's not how Pegasus works. To see the full picture, we recommend the recent analysis by Engadget.
According to Citizen Lab and the SHARE Foundation, Đokić's iPhone was hit using a zero-click exploit in 2026. Zero-click means the target doesn't tap a suspicious link, open a weird attachment, or do anything "wrong." The attack silently compromises the device in the background.
Đokić isn't a quiet bureaucrat hiding behind faculty bylaws. An architect and former dean of the Faculty of Architecture who has led the University of Belgrade since 2021, he became a high-profile defender of university autonomy and student demonstrators. In Serbia's heated political climate, pro-government outlets and officials framed him as a central force behind the protests, and in March 2026, authorities raided his offices and reportedly seized computers and servers. Đokić called the phone compromise a direct assault on his privacy, security, and the integrity of his office, framing it as intimidation meant to silence critical voices.
What makes this case hit even harder is who else surfaced in the same October 2026 research update. Rade Bajić, a senior prosecutorial associate at Serbia's Public Prosecutor's Office for Organized Crime who worked on the "Generalštab" corruption probe involving a proposed property project in Belgrade tied to Jared Kushner, received Apple Threat Notifications in August. Citizen Lab treats those Apple alerts as high-confidence indicators of targeting with mercenary spyware, though forensic analysis of Bajić's artifacts remained ongoing.
Putting a university rector and an organized-crime prosecutor in the same spyware report sends a clear message. Once surveillance crosses from street activists into universities and prosecutorial offices, the threat isn't just about monitoring protests anymore. It's about chilling institutional pushback.
A Pattern That Started Long Before October
If you treat this infection as a one-off, you're missing the bigger picture. Serbia has a long, documented record of surveillance controversies stretching back over a decade, involving outside vendors like Hacking Team, FinFisher, Intellexa, and NSO Group, alongside homegrown tools.
By September 2026, the SHARE Foundation reported that at least 14 people in Serbia had been targeted with advanced spyware since the start of the year, calling it the largest documented wave of such surveillance in the country up to that point. Those targets included student protesters, activists, an opposition lawmaker, and a local opposition councilor, with cases clustering around the March 29, 2026 local elections. Forensic work by SHARE, Citizen Lab, and Amnesty International's Security Lab documented both Pegasus and a newer version of NoviSpy, a spyware family that first surfaced in Serbia in 2024 and has been linked by Amnesty's Security Lab to state authorities.
With the October 2026 cases involving Đokić and Bajić, researchers put the public tally of known civil society and public-figure targets in Serbia at least at 16.
Now, attribution is tricky, and we have to be straight about what forensic reports prove and what they don't. Forensic labs like Citizen Lab and Amnesty International can identify signatures and artifacts of spyware like Pegasus or NoviSpy on a device, and Apple can warn users of state-sponsored or mercenary targeting. What a forensic artifact alone doesn't automatically hand you is a signed confession naming the operator behind the keyboard. Serbian authorities and the Security Information Agency (BIA) have denied wrongdoing in past cases and dismissed surveillance allegations as malicious or aimed at stoking instability.
Even so, the political shift that followed makes the story impossible to ignore. On October 25, 2026, the student-backed Students' List defeated Aleksandar Vučić's Serbian Progressive Party in snap parliamentary elections, winning 140 of 250 seats and convening a historic inaugural parliament session in mid-November. That outcome doesn't erase the surveillance that happened before the vote. If anything, it turns past spyware allegations into an urgent governance test for incoming lawmakers trying to reform oversight and intelligence agencies without repeating old abuses.
What Mercenary Spyware Actually Sees On A Phone
People often ask whether encrypted messaging apps protect you from spyware. Kinda—but only up to a point.
End-to-end encryption protects messages in transit between devices. Once mercenary spyware like Pegasus implants itself on a phone's operating system, it sits right on the device where you read those messages. From there, an attacker can potentially access messages, call logs, contacts, photos, location data, and app contents, or turn on the microphone and camera.
That's why defenders who've worked on high-risk cases emphasize a blunt reality: no consumer phone is 100% immune to a well-funded attacker with zero-day exploits. What matters is raising the cost of compromise, keeping clean forensic trails, and knowing what to do the moment a warning appears.
Why People Miss The Warning Signs
Most folks don't get hacked because they're careless; they get targeted because of who they know, what they investigate, or what they organize. Still, two common mistakes make bad situations worse:
- Ignoring or wiping a device in panic. If you get an Apple Threat Notification or suspect spyware, factory-resetting immediately without talking to trusted security researchers can wipe useful forensic evidence.
- Relying on "antivirus" apps. Standard mobile antivirus apps aren't built to stop nation-state or commercial zero-click spyware on iOS or Android.
Practical Steps If You Face High-Risk Targeting
You don't need to live like a spy to take smart precautions, especially if you're a journalist, researcher, activist, lawyer, or public official working on sensitive issues. Start with moves that actually raise the bar:
- Turn on Lockdown Mode if you're at elevated risk. Apple's Lockdown Mode severely restricts certain features, attachments, and web technologies to shrink the attack surface against mercenary spyware. It's inconvenient for everyday social browsing, sure, but for high-risk targets it's one of the strongest built-in defenses available.
- Keep operating systems updated promptly. Vendors patch vulnerabilities constantly, and running outdated software leaves known holes wide open.
- Treat any threat notification as urgent. Citizen Lab advises treating an Apple Threat Notification as a high-confidence indicator of likely mercenary spyware targeting and reaching out to vetted digital security experts rather than trying to guess what happened on your own.
- Separate sensitive work from personal habits. Keep high-risk communications, sources, and scheduling off casual devices when possible, and use hardware security keys for critical accounts.
In the end, what happened to Vladan Đokić shows why digital security isn't a niche IT topic anymore. When a university rector's phone becomes a battleground during student protests, free speech, academic freedom, and democratic accountability are all sitting inside that pocket. Check your device security settings today, keep sensitive conversations out of reach of compromised endpoints, and back up critical records offline before a crisis forces your hand.


